
Understand the threat. Build the defense.
MAG212 explains the attacks and vulnerabilities that matter in plain language, then shows you what to do about them. Every analysis cites its sources and ends with practical steps you can take today, whether you protect a family, a small business or an enterprise network.
Latest analysis
New explainers on the vulnerabilities and incidents security teams are dealing with right now: what happened, who is affected and what to do.
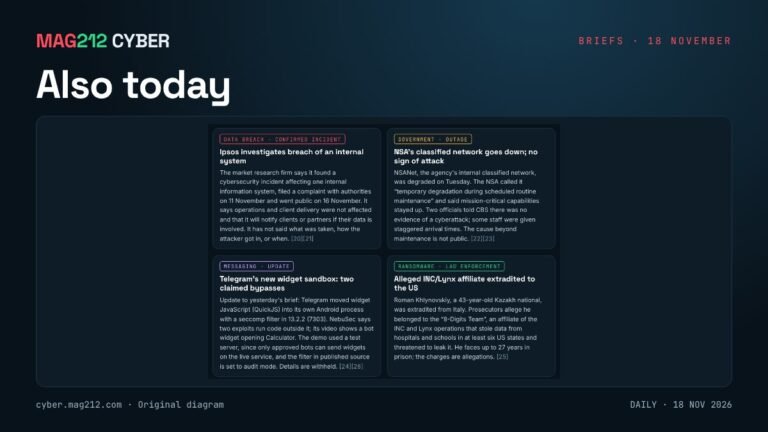
Also Today: Ipsos Investigates Breach, NSA Network Outage, Telegram Widget Sandbox Bypasses and an INC/Lynx Extradition
Ipsos is investigating a breach of one internal system, the NSA’s classified network suffered an outage officials say was not an attack, researchers claim two bypasses of Telegram’s new…
Read the analysis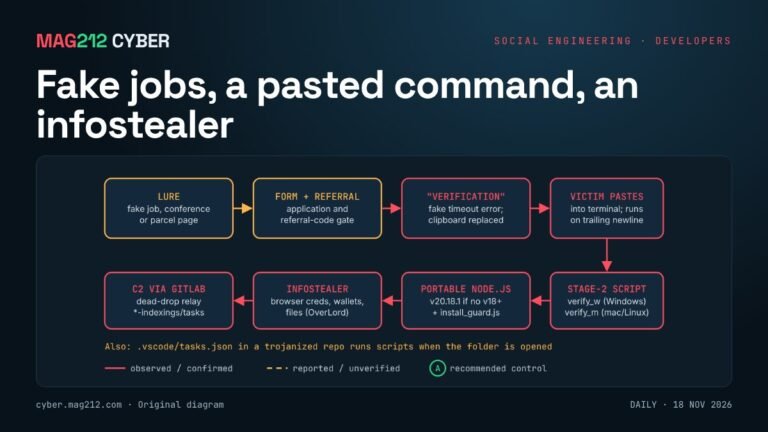
Trigram Campaign: Fake Recruiters, a Pasted Command and an Infostealer Aimed at AI and Blockchain Developers
Stormshield’s Trigram campaign impersonates about 50 AI, blockchain and tech brands with fake job offers, a fake conference and…
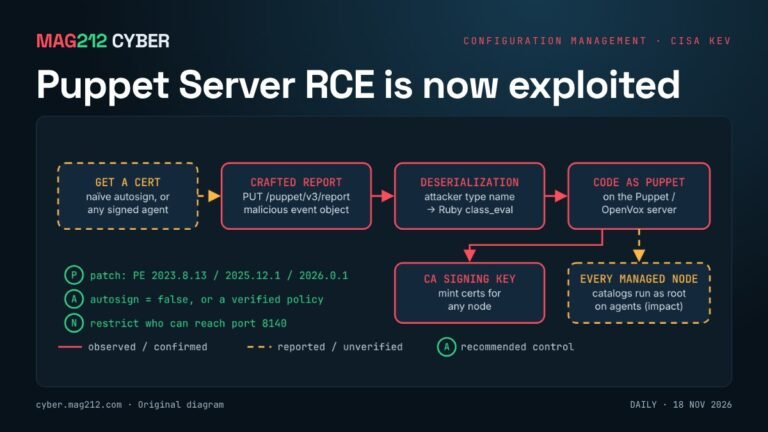
Puppet Server RCE (CVE-2026-115731) Is Now Exploited: How the Report Deserialization Flaw Works and How to Fix It
CISA added CVE-2026-115731, a report-deserialization flaw in Puppet Server and OpenVox, to its Known Exploited Vulnerabilities…
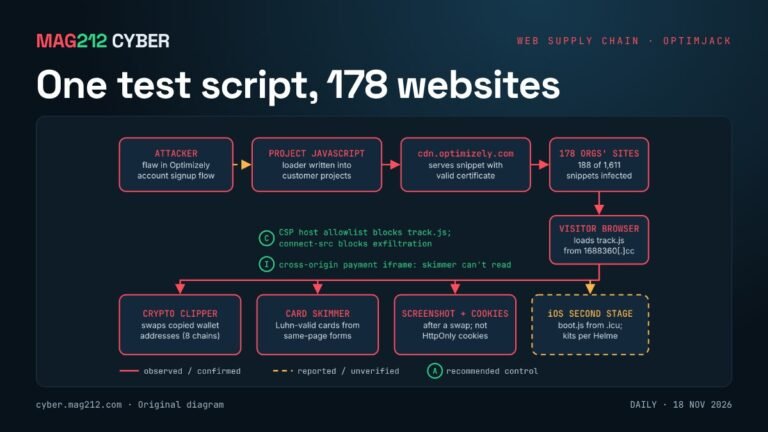
OPTIMJACK: How a Hijacked Optimizely Script Served a Crypto Clipper, Card Skimmer and iPhone Exploit Loader to 178 Websites
On 16 November 2026 an attacker abused a flaw in Optimizely Web Experimentation to inject malicious JavaScript into customer…
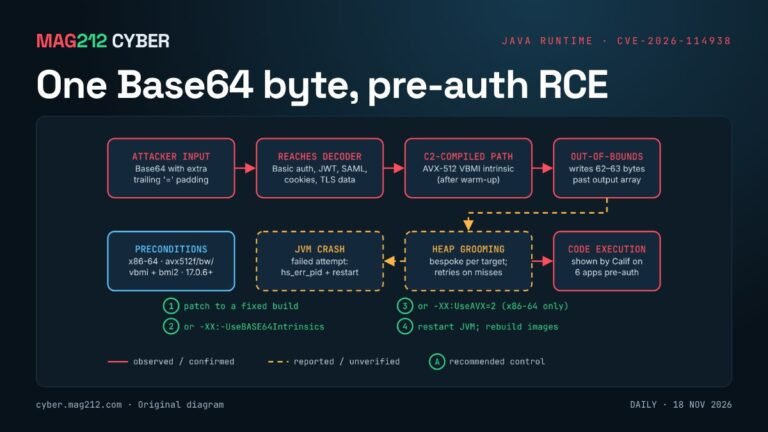
Java4Shell (CVE-2026-114938): How One Base64 Byte Leads to Pre-Auth RCE in Jira, Jenkins and Keycloak, and How to Patch
A memory-corruption bug in Java’s AVX-512 Base64 decoder lets malformed input write past a buffer. Calif used it for login-free…
Also Today: Telegram Widgets RCE Dispute, Retadup Worm Returns, SANSAR GPU Miner and the BIS AI Remote-Access Rule
Telegram’s new widgets drew RCE demonstrations and a Kaspersky malware warning, the Retadup worm is back with CoffeeLoader,…
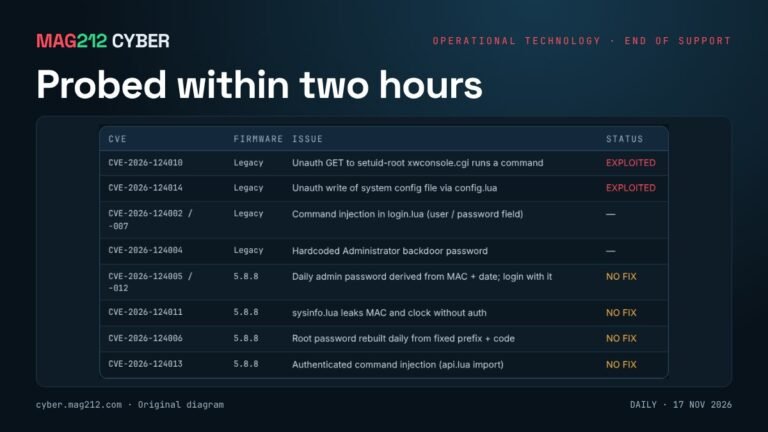
Copeland XWEB EVO Refrigeration Controllers: 14 Root Flaws, Two Exploited Within Hours, Five Never to Be Fixed
VulnCheck disclosed 14 vulnerabilities in Copeland (Dixell) XWEB EVO refrigeration controllers, each giving root on test systems.…
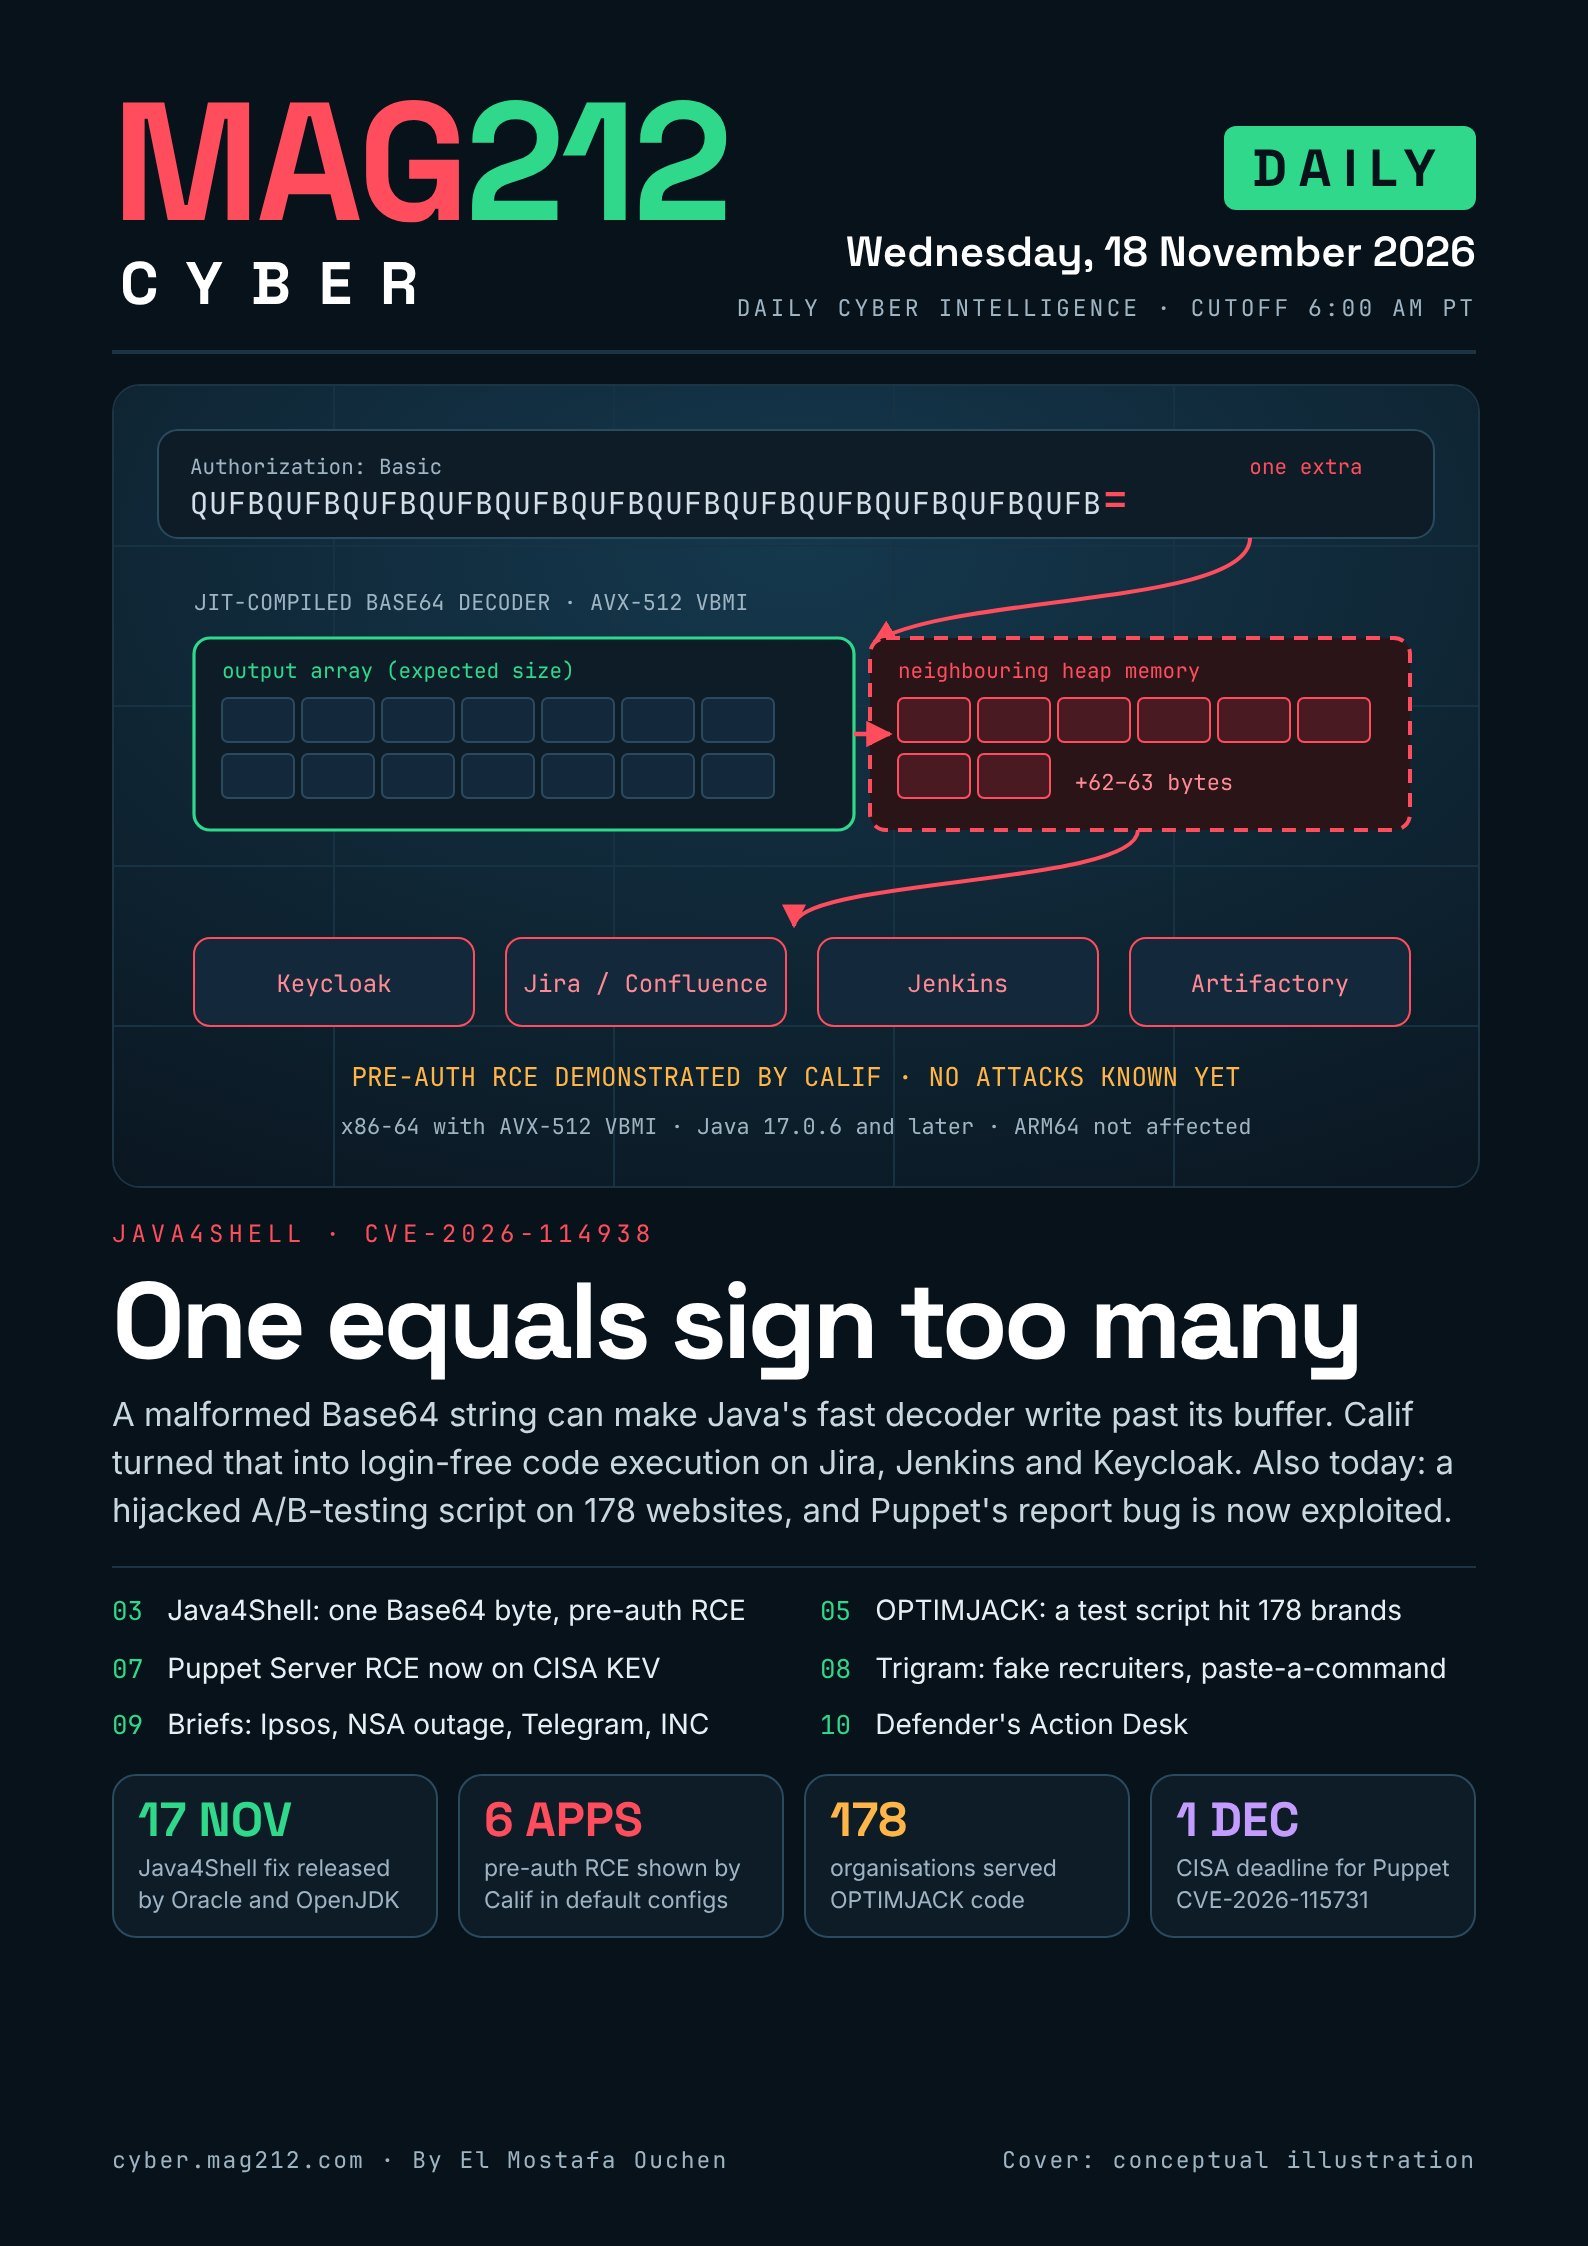
One Equals Sign Too Many: MAG212 CYBER Daily, November 18, 2026
Java4Shell (CVE-2026-114938) turns one malformed Base64 string into pre-auth code execution on Java apps running on AVX-512 servers; fixes shipped 17 November. A hijacked Optimizely script hit visitors of 178 organisations, Puppet’s report bug is now exploited, and Trigram lures developers into pasting an infostealer.
Each issue pairs every story with a defensive field guide: an architecture diagram, the controls that actually help and the steps to verify you are protected.
Free security tools
Practical tools built for everyday security decisions. They run in your browser, and the sensitive ones never send your data anywhere.
Learn cybersecurity step by step
Structured learning paths that take you from the basics to professional skills, using our articles, cheat sheets and tools along the way.
Pick the path that fits you, from staying safe online to professional security skills, and track your progress as you go.
Start a learning path →About MAG212
MAG212 is an independent cybersecurity publication founded and edited by El Mostafa Ouchen, an IT and cybersecurity professional with more than 20 years of experience in enterprise networking, systems administration and digital infrastructure.
Every story is checked against primary sources, which we link so you can verify them yourself. The goal is defense: helping readers understand threats and protect what matters.
About us · Editorial policy · Books by the editor